Policies
The principles of operation of the sections Firewall, Application Control, Content Filter, and RateTraffic LimitingShaping with connected UTM are identical. Consider it using the Firewall section as an example.
Firewall
The Safe Center firewall contains only FORWARD and INPUT tables.
An example of adding rules in Safe Center: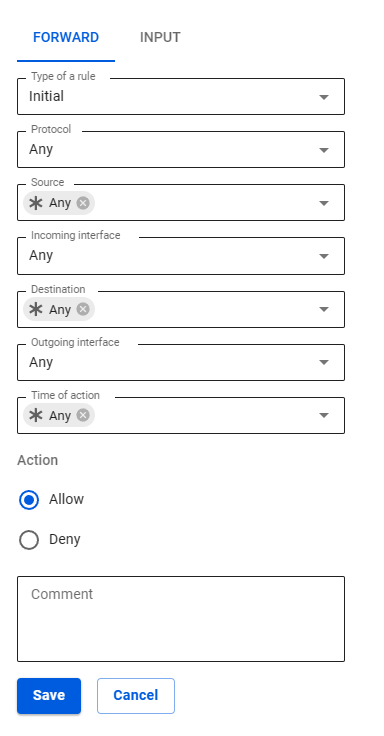
At Safe Center
The Forward rules created in Safe Center are displayed in two tables: Start RulesInitial and End RulesFinal. These tables shareare divided by Local Rules on SafeUTM servers.
An example of an empty table:
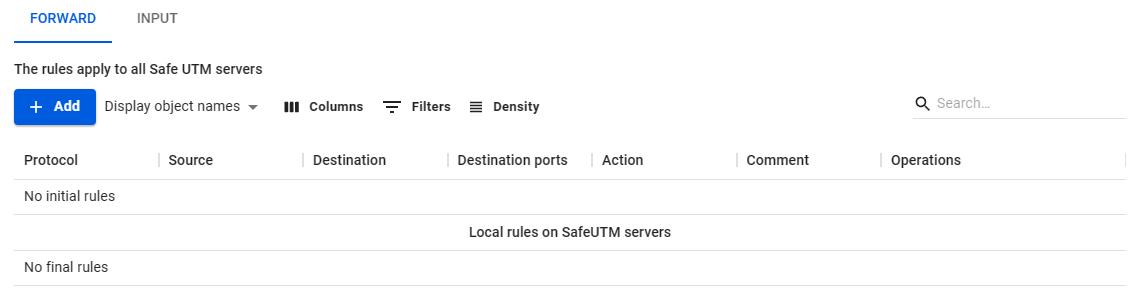
An example of a completed table:

Local rules on SafeUTM servers are not visible in the Safe Center interface. To view, go to the Servers section, click on the eye icon in the line with the required SafeUTM, and go to the Firewall section.
In order for the created rule to be included in the Initial rules table, specify the Initial value in the Rule type line. If you want to place the rule in the EndFinal Rulesrules table, select the EndFinal value.
You cannot move rules between the StartInitial Rulesrules and EndFinal Rulesrules tables.
In SafeUTM
The table in SafeUTM is visually divided into three parts: top, middle, and bottom.
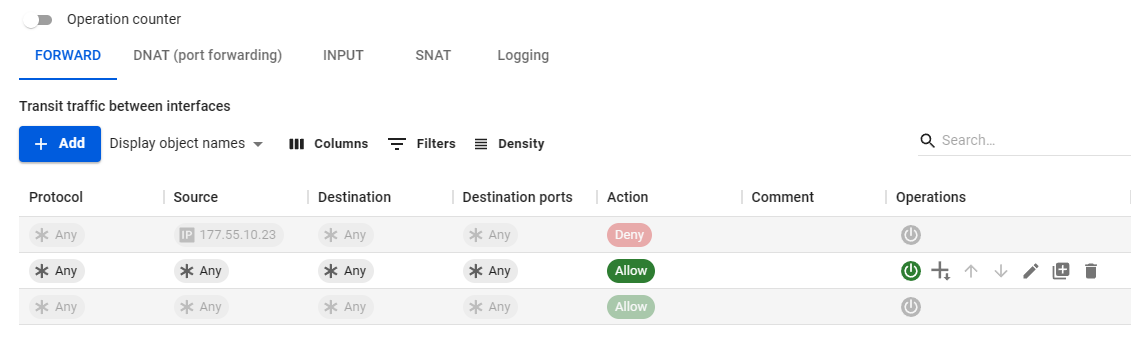
The rules from the connected Safe Center are transferred to the upper and lower parts. These rules cannot be managed in SafeUTM. The top part corresponds to the StartInitial Rulesrules table in the Safe Center. The lower part - the table EndFinal rules.rules.
The middle part is created by the UTM administrator in UTM itself and is not visible in the Safe Center interface.