
Deployment options
DependingSafeDNS onShield supports multiple deployment options to accommodate different network topologies. This section describes the client'smost networkcommon topology, there can be numerous deployment schemes. Below are examples of typical solutions.scenarios.
For ISPs
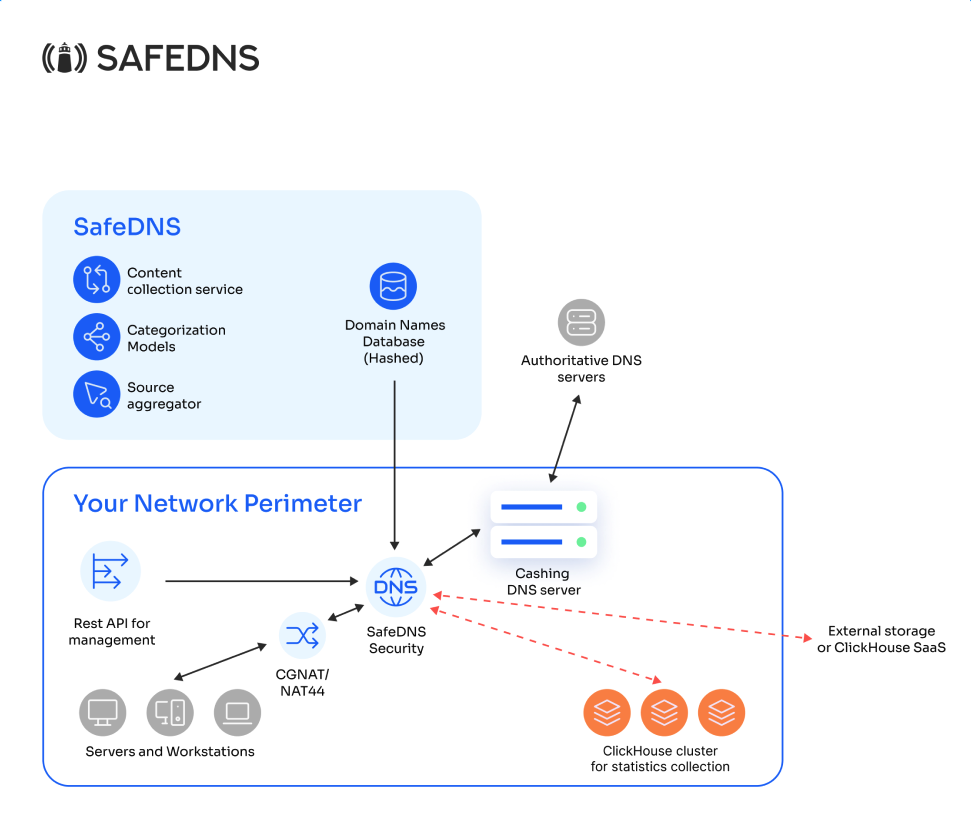
This deployment option is used in largeISP networksnetworks, where NAT separates end users are behind NAT in relation tofrom the client'son-premises mainDNS equipment,infrastructure, making it impossible to identify them solely by their individual IP addresses.
For corporate clients
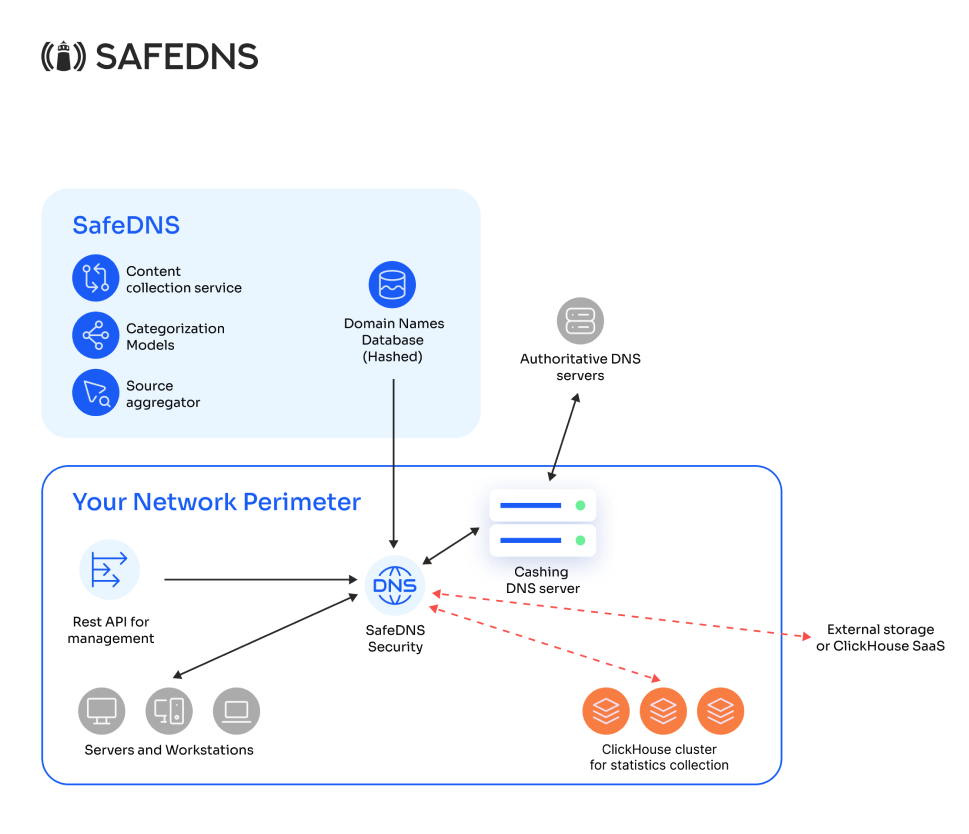
or
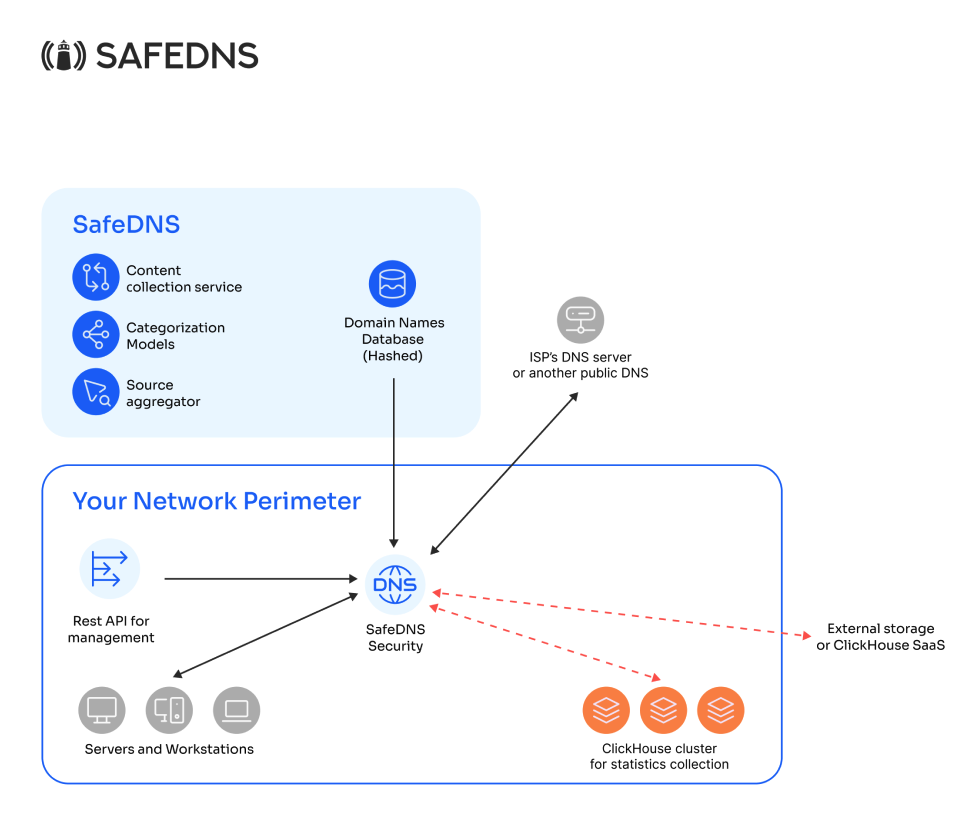
This setupdeployment option is used in corporate networks where the end userusers can be identified by their individual IP addressaddresses at the deploymentpoint locationwhere ofSafeDNS ourShield solution.is deployed. Depending on whether the companyorganization has its own caching DNS server, requests are either proxiedforwarded to itthat server or to an external infrastructureresolver, (ISPs'such as an ISP’s DNS or anya public DNS,DNS suchservice as(e.g., 1.1.1.1 or 8.8.8.8).